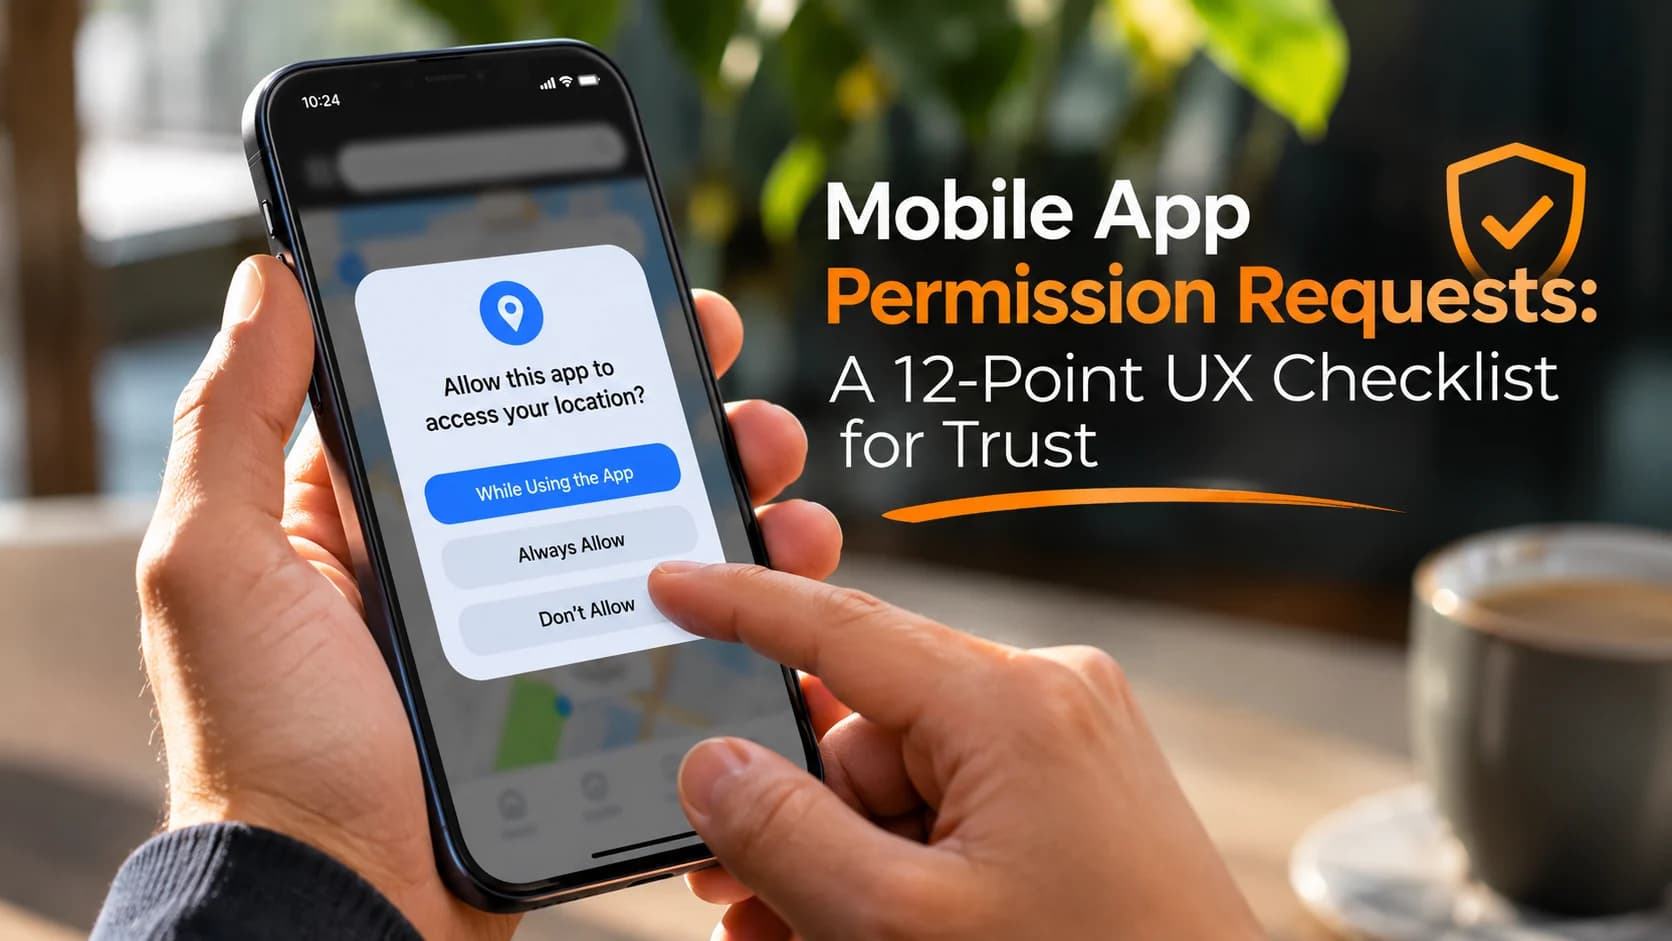
A permission prompt can be the first moment a customer questions whether your mobile app deserves their trust. When someone opens an app to book a service, upload a product photo, or track an order, an unexpected request for location, camera, contacts, or notifications can interrupt the task. Good permission UX makes the purpose clear, asks at the right time, and keeps the experience useful when the answer is no.
This mobile app permission requests UX checklist helps business owners and product teams review iOS and Android experiences before launch or during a redesign. It focuses on practical choices, not tactics for pressuring users into accepting every request.
Why permission requests are a UX decision
Operating-system permissions protect sensitive data and device capabilities. They also introduce decisions into a customer journey. If a delivery app asks for location before showing what it does, users may hesitate. If the same app offers “Use my location” beside a manual address field, the request becomes understandable. The goal is to match the request to a useful action.
Apple's Human Interface Guidelines on privacy advise requesting access when the app needs it and explaining the purpose clearly. Android's app-permissions best practices similarly recommend contextual prompts, minimal permissions, and graceful handling of denial. Specific APIs and prompts differ by operating system and permission type; confirm the current platform requirements during implementation.
12 checks for better mobile app permission UX
1. Inventory every permission your app may request
Create a table of protected resources, the feature that needs each resource, the moment it is needed, and whether it is essential or optional. Include camera, microphone, location, notifications, contacts, photos, and any other relevant capabilities. Review third-party SDKs as well; a dependency can introduce access requirements that product stakeholders never intended.
Acceptance check: Each requested permission has a documented feature, reason, and fallback.
2. Eliminate requests you do not need
Sometimes the best permission dialog is no dialog. A customer might type an address instead of sharing live location, choose a specific photo through a system picker rather than grant broad library access, or enter a phone number instead of sharing contacts. Explore privacy-preserving platform alternatives before adding a permission to the product scope.
Acceptance check: The team has considered a less intrusive way to complete the same task.
3. Ask at the point of use, not automatically at launch
For a marketplace app, request camera access after the customer taps “Take photo.” For a local search feature, ask for location after “Find near me.” This gives the user a clear reason for the system dialog. An exception may be a capability essential to the app's primary function, but even then the value should be immediately apparent.
Acceptance check: A first-time user can predict why the request appears.
4. Explain the immediate benefit in everyday language
Compare “Location permission is required for optimal functionality” with “Use your location to find nearby pickup points.” The latter explains the result rather than merely naming a capability. Avoid jargon, vague assurances, or promises that do not match the actual data use. Keep system purpose strings accurate and concise.
Acceptance check: The explanation names what the user can do after granting access.
5. Use pre-permission screens sparingly
A short explanation can help when a request is unfamiliar. But an extra screen before every system prompt creates more friction. If the action itself provides enough context, the operating-system dialog may be sufficient. Never imitate system alerts or create misleading consent screens. Review the applicable app-store guidance before adding custom permission education.
Acceptance check: Any extra screen provides necessary information rather than simply encouraging an “Allow” tap.
6. Provide a usable denial path
Declining an optional permission should not break unrelated functionality. A delivery customer can search by postcode instead of sharing location. A shopper can browse without promotional notifications. A profile editor can upload a previously saved image instead of opening the camera. Show what is unavailable and offer an alternative where possible.
Acceptance check: Core tasks still work when optional access is denied.
7. Separate device access from communication preferences
Notification permission is not a substitute for a thoughtful messaging strategy. Customers may want appointment reminders but not promotional messages. Provide clear in-app preferences for relevant categories, and ensure your data practices and communications meet applicable consent requirements. Do not bundle unrelated marketing decisions into a necessary product action.
Acceptance check: People understand which messages they can receive and how to change those choices.
8. Respect a previous “No”
Repeatedly nagging people after denial undermines trust. Revisit the topic only when someone returns to a feature that genuinely needs the capability. If the system will not present another prompt, explain the optional settings path instead of pretending the app can force a fresh request. Avoid persistent banners that make unrelated features difficult to use.
Acceptance check: The app does not repeatedly interrupt users about an optional permission they already declined.
9. Handle limited, temporary, and revoked access
Depending on platform and permission type, users may allow approximate location, select only certain photos, grant one-time access, or later change the decision in device settings. Your implementation should check the current state when needed rather than assume access remains available forever. Test a feature when permissions change while the app is running or between sessions.
Acceptance check: The feature handles restricted or revoked access without a crash or confusing blank state.
10. Write actionable error messages
“Permission denied” describes a technical condition, not a useful next step. Instead, explain the consequence and available options: “We couldn't open the camera. Choose a photo instead, or enable camera access in your device settings.” Use direct language without blaming the customer. If no fallback exists, explain exactly which feature is unavailable.
Acceptance check: Every denial state tells the user how to continue or recover.
11. Test real tasks with real people
Watch users complete common tasks with access granted, denied, limited, and later revoked. Ask what they expected before each prompt and whether the explanation was understandable. Include accessibility checks, readable text, screen-reader behavior, and tap targets. A structured UI/UX design review can reveal permission friction while changes are still inexpensive to make.
Acceptance check: Testing covers successful and unsuccessful permission paths, not just the ideal demonstration.
12. Measure task success, not just permission acceptance
A high “Allow” rate does not prove a good experience. Where appropriate and privacy-respecting, measure the attempted feature, prompt outcome, fallback use, and completed task. Review support tickets and abandonment points alongside analytics. A permission flow that helps people finish their work without unnecessary access may be more valuable than one that simply maximizes grants.
Acceptance check: Your success measure reflects customer task completion and informed choice.
Example: location and notifications in a booking app
Consider a mobile app for booking local appointments. On its first screen, customers can choose “Search by city” or “Use my location.” If they choose the second option, the app explains that location will identify nearby providers and then presents the appropriate system request. If they decline, the city search remains available. Booking itself does not depend on location access.
After a customer books, the app may offer appointment reminders. That is a natural point to explain notification value and request permission where required. The customer should still be able to view booking details inside the app without notifications. This is a small example of customer journey optimization: each decision supports the next task rather than interrupting it.
What to specify before developers begin
Permission behavior belongs in the requirements document, not in a last-minute release checklist. For each capability, record the triggering action, system API, explanation text, optional or essential status, denied state, fallback, settings recovery, and relevant test cases. Assign responsibility for approving the wording and verifying the implementation.
For example, a testable camera requirement might read: “When a customer taps ‘Take photo,’ the app requests camera access if needed. If access is declined, the customer can select an existing photo or return to the form without losing their entries.” That is more precise than “Handle camera permissions.”
During early product planning, define the smallest useful set of features and permissions. An app and platform development plan should map roles, workflows, and access needs before committing to a complex first release.
Common mistakes to catch before release
- Prompting for everything at once: Several unrelated dialogs appear before users experience any value.
- Overly broad requests: The app seeks more data than the selected feature requires.
- Unclear wording: The explanation uses generic phrases such as “better experience.”
- Broken denial handling: The feature fails silently or blocks unrelated tasks.
- Manipulative prompts: A custom screen disguises the choice or repeatedly pressures users.
- Platform assumptions: The team tests one OS version and assumes all permission states behave identically.
A practical permission test matrix
For every supported operating system and major app flow, test first request, grant, denial, limited access when applicable, revocation, return visits, and settings recovery. Record what the customer sees, whether their work is preserved, and whether they can complete the task. Include low-connectivity scenarios where they affect the feature, since network failures can otherwise be mistaken for permission problems.
Prioritize issues that prevent checkout, booking, communication, or other high-value actions. After release, revisit the flows when operating-system behavior changes or customer feedback identifies new friction. Permission UX is an ongoing product-quality responsibility, not a one-time dialog design.
Make permission decisions part of a trustworthy app
Good permission UX follows a simple principle: ask only when necessary, explain the benefit, respect the answer, and keep the customer moving. Applying that principle requires product planning, design, development, and testing to work together.
If you are planning a new mobile product or improving an existing app, DesDevSol can help scope permission-sensitive journeys, prototype clear interactions, and implement the approved behavior through its mobile application development service. Share your core customer tasks and current friction points to start a focused discussion.